Vesper Signal: Spot the attack before it dictates your next move. Sentinel adds automatic monitoring to Security Center. It can detect password attacks, FTP/SSH exploits and foreign virus installations, record their source IP and buy you time with a protection pause. It keeps working while you are logged out.
What you need
- An active Security Center subscription for the server you want to protect.
- The Sentinel add-on. It normally costs $5,000 in game money per week, on top of the $2,000 base subscription. The App Store shows the offer, payment account and next charge.
- Both applications downloaded and Sentinel explicitly started.
- The matching protection program actually running, with enough CPU and RAM available.
| Incoming attack | Required running protection | Attacker's tool |
|---|---|---|
| Normal server crack | Hasher | Cracker |
| FTP/SSH exploit | Firewall | Exploit being used |
| Ordinary foreign virus installation | Antivirus | Virus being installed |
A strong Antivirus does not replace a Hasher against password attacks. A Firewall protects against exploits. Software merely stored on disk is not running protection. Starting Antivirus and scanning for viruses are separate actions.
Three possible outcomes
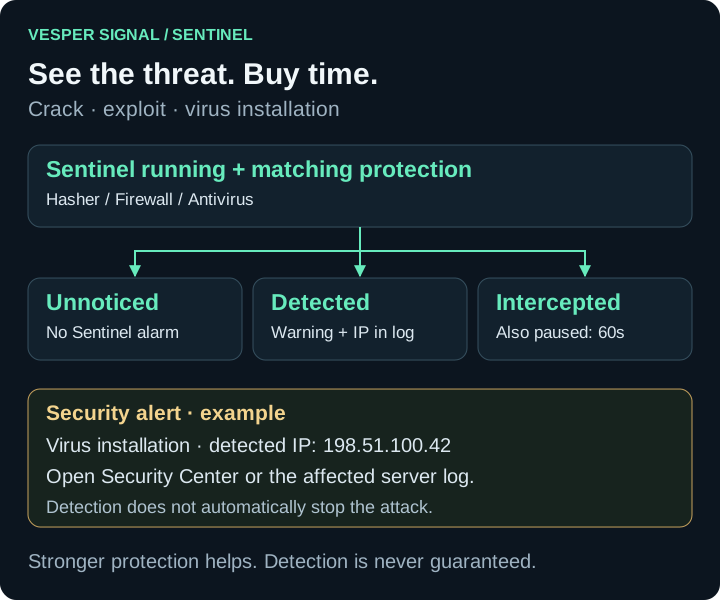
- Unnoticed: Sentinel produces no warning and the attack continues. Ordinary connections or game actions may still leave other traces.
- Detected: A desktop warning reports the attack. The defender receives its type, time, target server and the outgoing game IP used for that attack. The same IP is recorded in the target's server log. The attack continues unless another defense slows it.
- Intercepted: Alongside the warning and log entry, the attack pauses for 60 seconds. A virus installation does not take effect during that pause. Work resumes afterward unless something else interrupts it.
The warning appears even when Security Center is closed. Multiple events are grouped without taking over input in other windows. Security Center and Open log lead to the affected server, even if you are currently managing another one. Dismiss read warnings; reopen unread ones through the security icon. Earlier events remain available in Security Center.
You do not receive a real internet IP, an automatically identified player name, passwords or unknown tool versions. The detected game IP is a lead, not free access to the attacker.
Strength, risk and weaker Crackers
Stronger matching protection relative to the attacker's tool makes detection and interception more likely. Both remain a chance: detection is normally capped at 95% and interception at 60%. Without the appropriate running protection, that attack type cannot trigger a Sentinel hit.
For ordinary server cracks, your Cracker can be at most 2.0 versions below the Hasher. Cracker v3.0 can therefore attack Hasher v5.0; v5.1 is too high. Underpowered attempts take longer than equal-strength attacks and carry an additional detection risk against running Sentinel. This applies to normal server access. Bank and wallet access, and exploits, retain their separate requirements.
An ongoing attack is checked once at its first valid protection contact. Reloading, restarting Sentinel or briefly stopping it does not produce another chance against the same task. If Sentinel was initially stopped, starting it later can still catch ongoing attacks. Canceling and replacing an attack does not bypass an existing protection pause between that attacker and target.
Responding to a warning
Open the affected server. First distinguish detected from intercepted and check whether the displayed pause is still active. With Antivirus running, Lockdown can buy more time. During an actual control-node intrusion, investigate alarms, isolate services or reinforce nodes. An ordinary crack alone does not need the control node and does not activate these intrusion countermeasures.
Sentinel pauses do not extend Lockdown. After a virus warning, check the files later and run a cleanup scan if needed. Detecting an installation does not prove that the virus is already active, nor does an alarm remove an existing infection.
Limits and stopping
Sentinel adds no extra random check to DDoS attacks, Doom, bank/wallet access or control-node actions. Existing logins and infections remain. Capturing the control node ends current Sentinel pauses and suppresses new detection and interception for 120 seconds. Existing logs and events remain available.
Sentinel normally consumes 5% CPU and 32 MB RAM in addition to its protection programs. Stopping it releases those resources but does not cancel the subscription. A collective shares service state, resources and protection pauses. Task Manager shows the actual usage.
You can cancel the add-on separately at the end of its paid week. Without paid time, new checks stop; pauses already triggered may finish. After a disk reset, download the applications again and start Sentinel. Valid remaining paid time is preserved. Changing IP does not grant a new protection roll against the same attack.
Optional email
Under Settings → Notifications, enable email for attacks detected by Sentinel. It is off by default and requires a verified email address. The first alert is sent promptly; further events within ten minutes may be grouped. Collective alerts still require the appropriate permission.
The message includes server, time, detected attack type and known game IP, plus a desktop link. It may arrive after the 60-second pause has ended. Check the current game state and, if needed, your spam folder. In-game warnings work independently of whether email is enabled or delivered.
The companies in the game
Vesper Signal develops Sentinel as an add-on to Bastion Circuit's security platform. Both are fictional in-game companies with servers reachable through the App Store. Their infrastructure is strongly protected. Discovering their secrets requires finding your own leads and earning access; a subscription does not reveal their bank accounts or credentials.